User Roles via Entra ID
Starting with version 5.2.0, OPC Router 5 supports user authorization via user roles (see User Roles). The article "Connecting Microsoft Entra ID/Azure AD" describes how users from Microsoft Entra ID are created during login, how their local roles are imported from role claims, and how to disable automatic creation with "AZURE_AD_DISABLE_AUTO_PROVISION."
This page shows how to create the necessary app roles in Entra ID and assign them to users.
Creating OPC Router 5 User Roles in Entra ID
The following steps require a Microsoft Entra ID (formerly Azure AD) connection (see Connecting Microsoft Entra ID).
Open your Microsoft Entra ID tenant via the Microsoft Entra Admin Center.
You can also create user roles via the Microsoft Azure Portal, but assigning roles is only possible in the Microsoft Entra Admin Center.
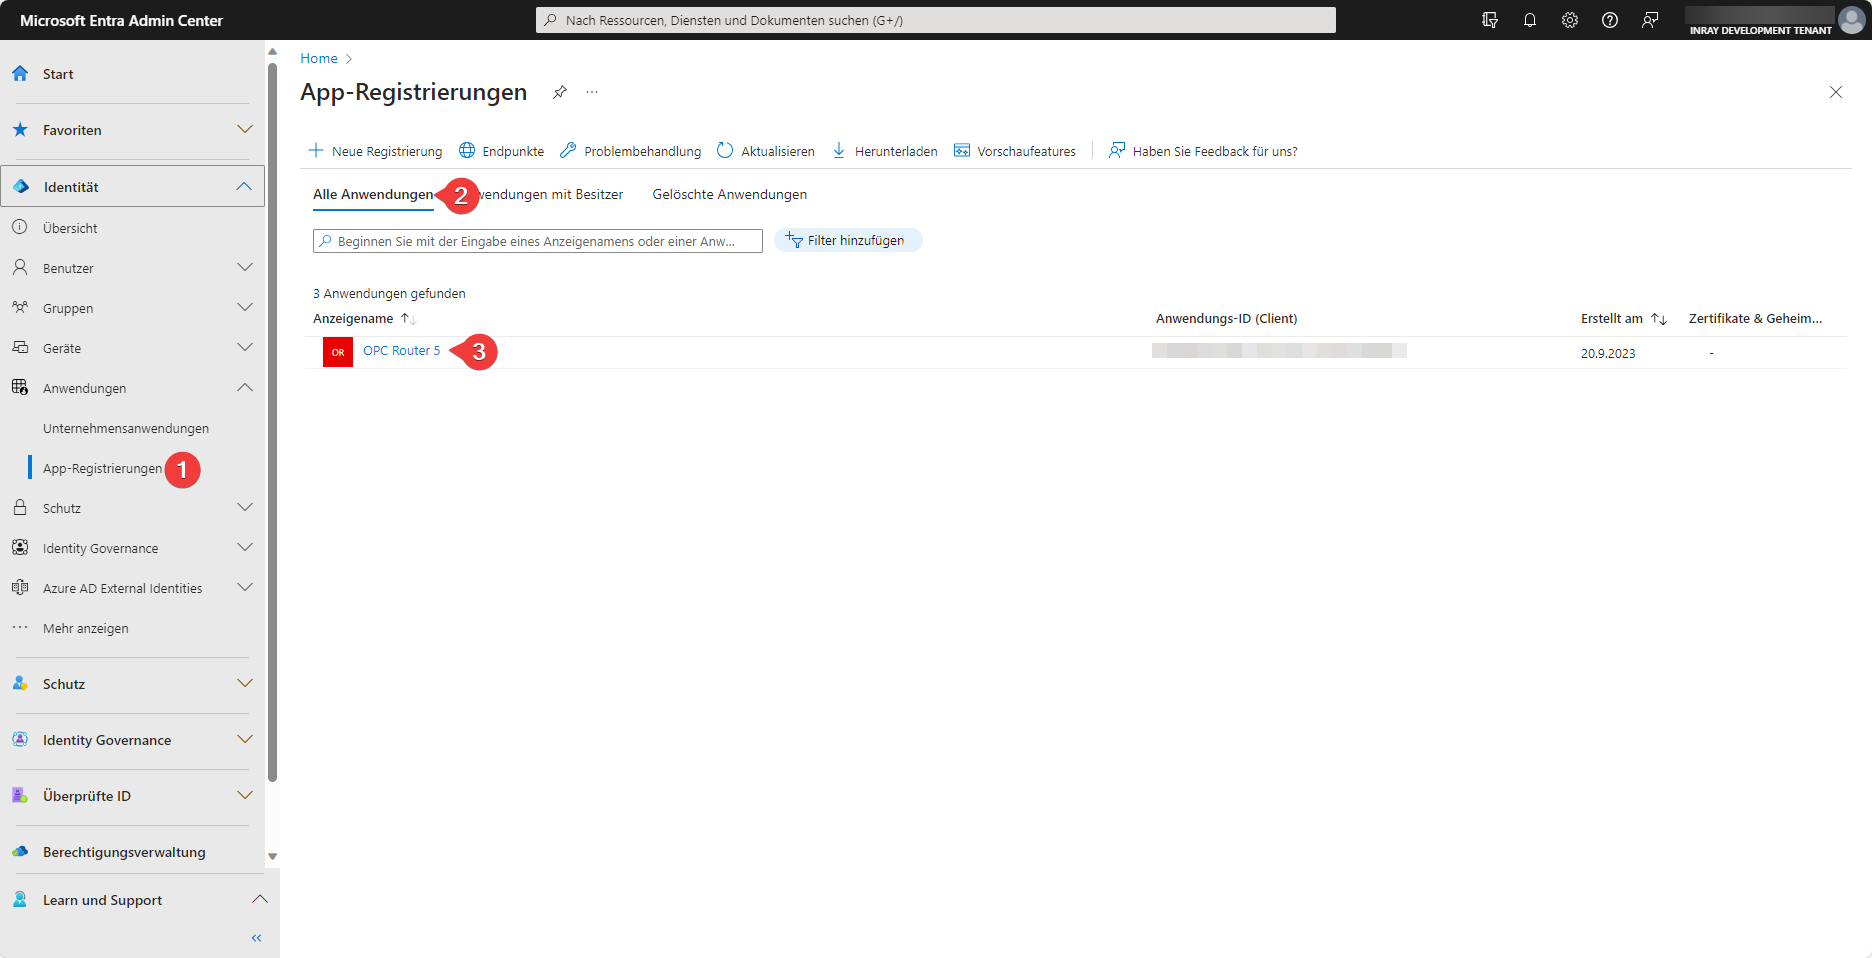
Now, under the App Registrations (1) tab, navigate to the All Applications (2) section and locate your application registration (3).
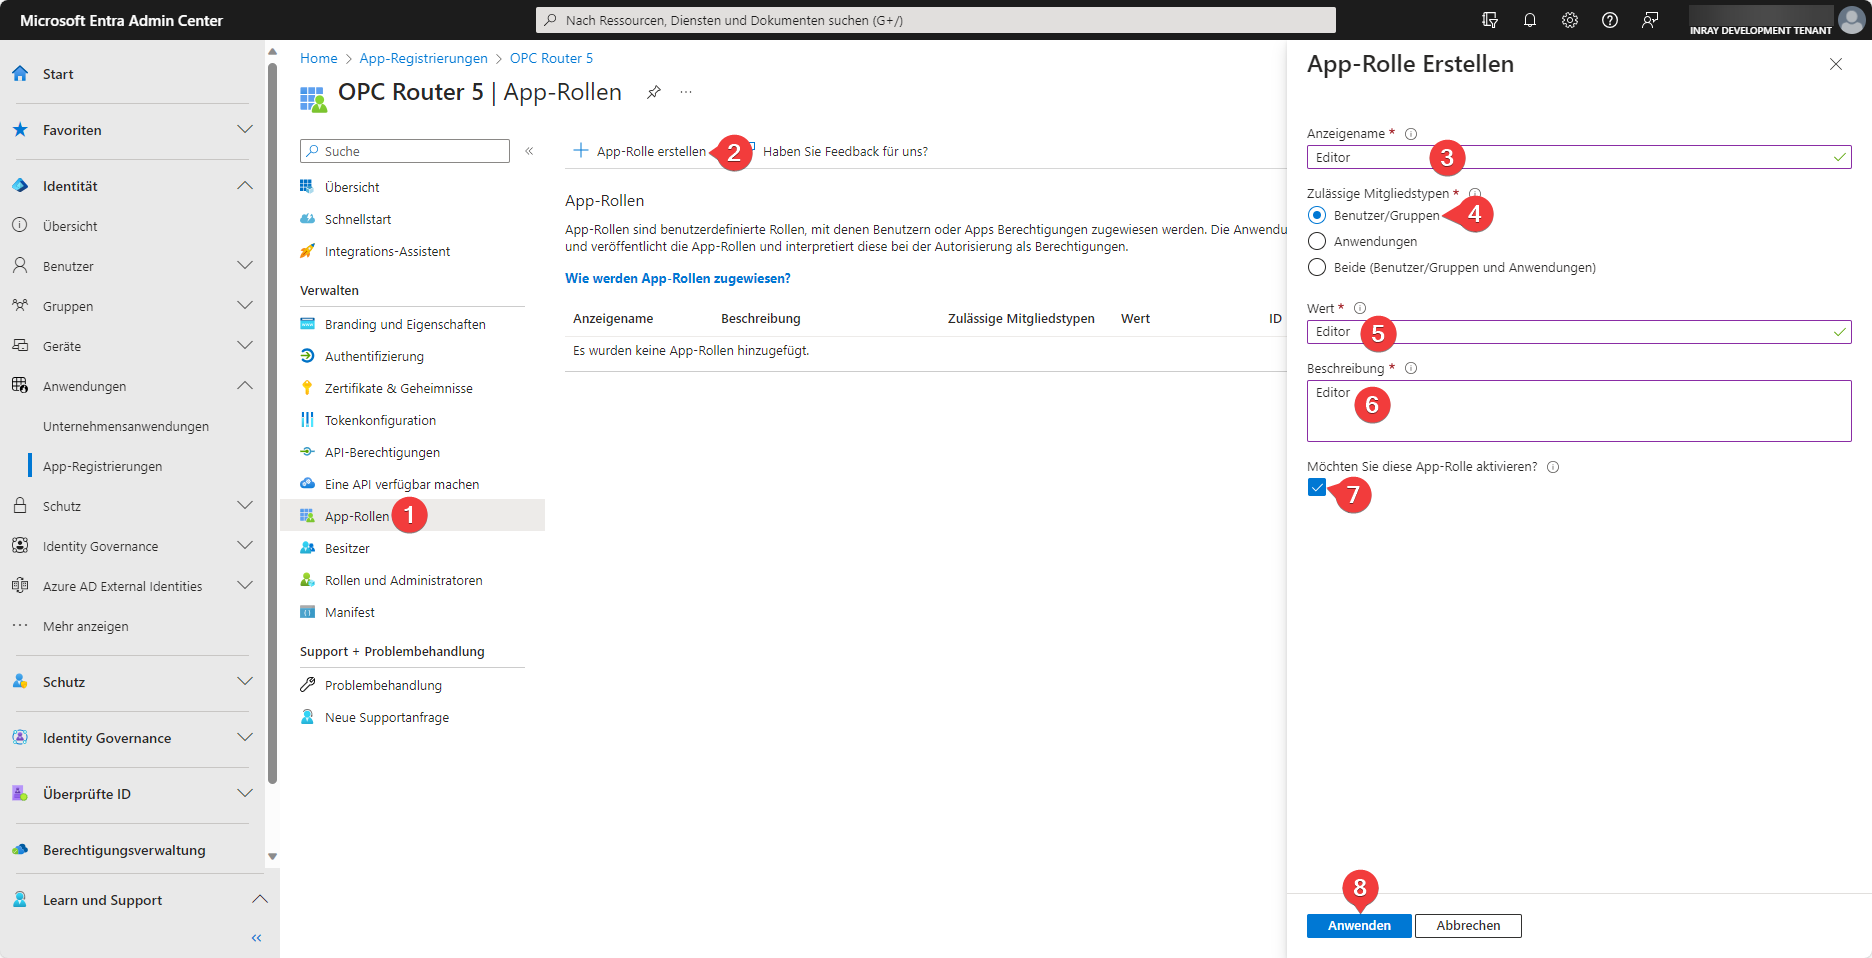
To add an app role, navigate to the App Roles (1) tab and select Create App Role (2). Select a display name (3) and choose Users/Groups (4) as the allowed member types. Under Value (5), enter the role that corresponds to the role in OPC Router 5.
Currently, only Admin, Editor, and Observer are permitted as values (5) for roles (see User Roles); while any other values do not trigger errors, they also have no permissions. These three values are predefined and cannot be renamed or extended; the claim from which OPC Router reads them is also the default role claim and cannot be configured. The Display Name (3) of the app role is unaffected by this and can be chosen freely—only the value is decisive.
Next, you must enter a Description (6) and ensure that the app role is enabled (7); the role can then be created by clicking Apply (8).
Create three roles in this manner with the values Admin, Editor, and Observer.
Assign app roles to users
The following steps assume that user roles for Admin, Editor, and Observer have been created.
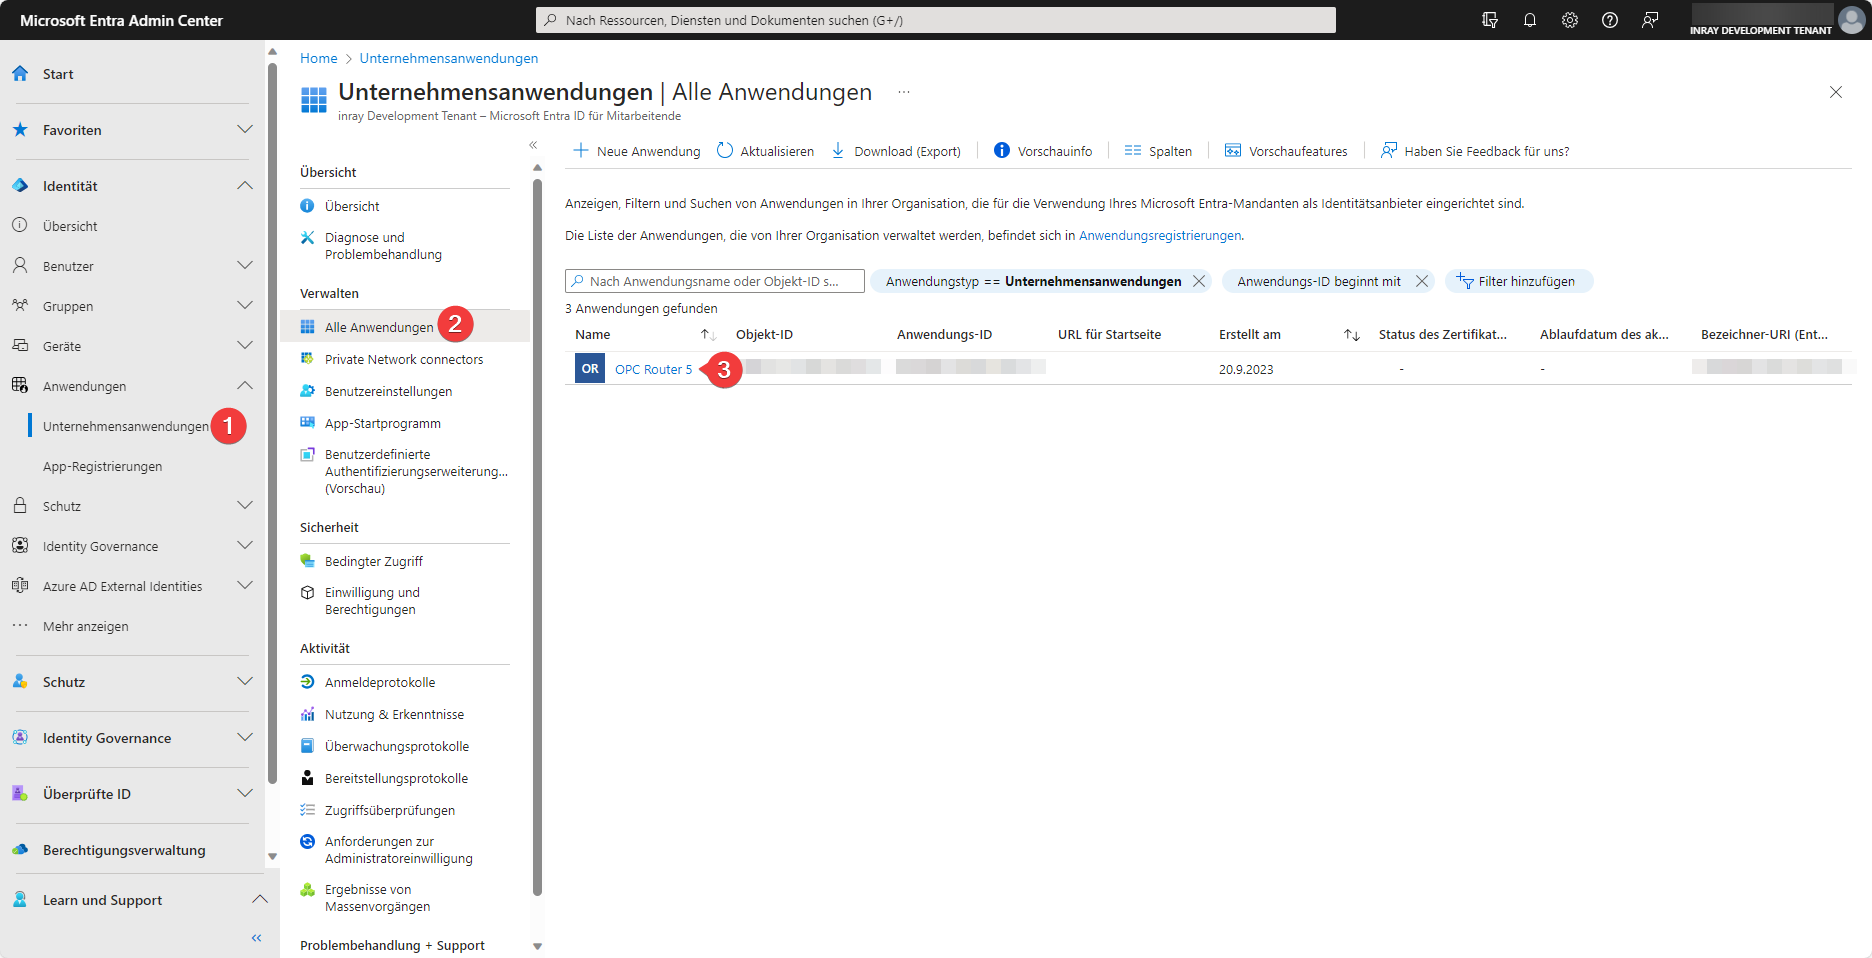
In the Microsoft Entra Admin Center, navigate to your application (3) under the Enterprise Applications (1) tab and the All Applications (2) section.
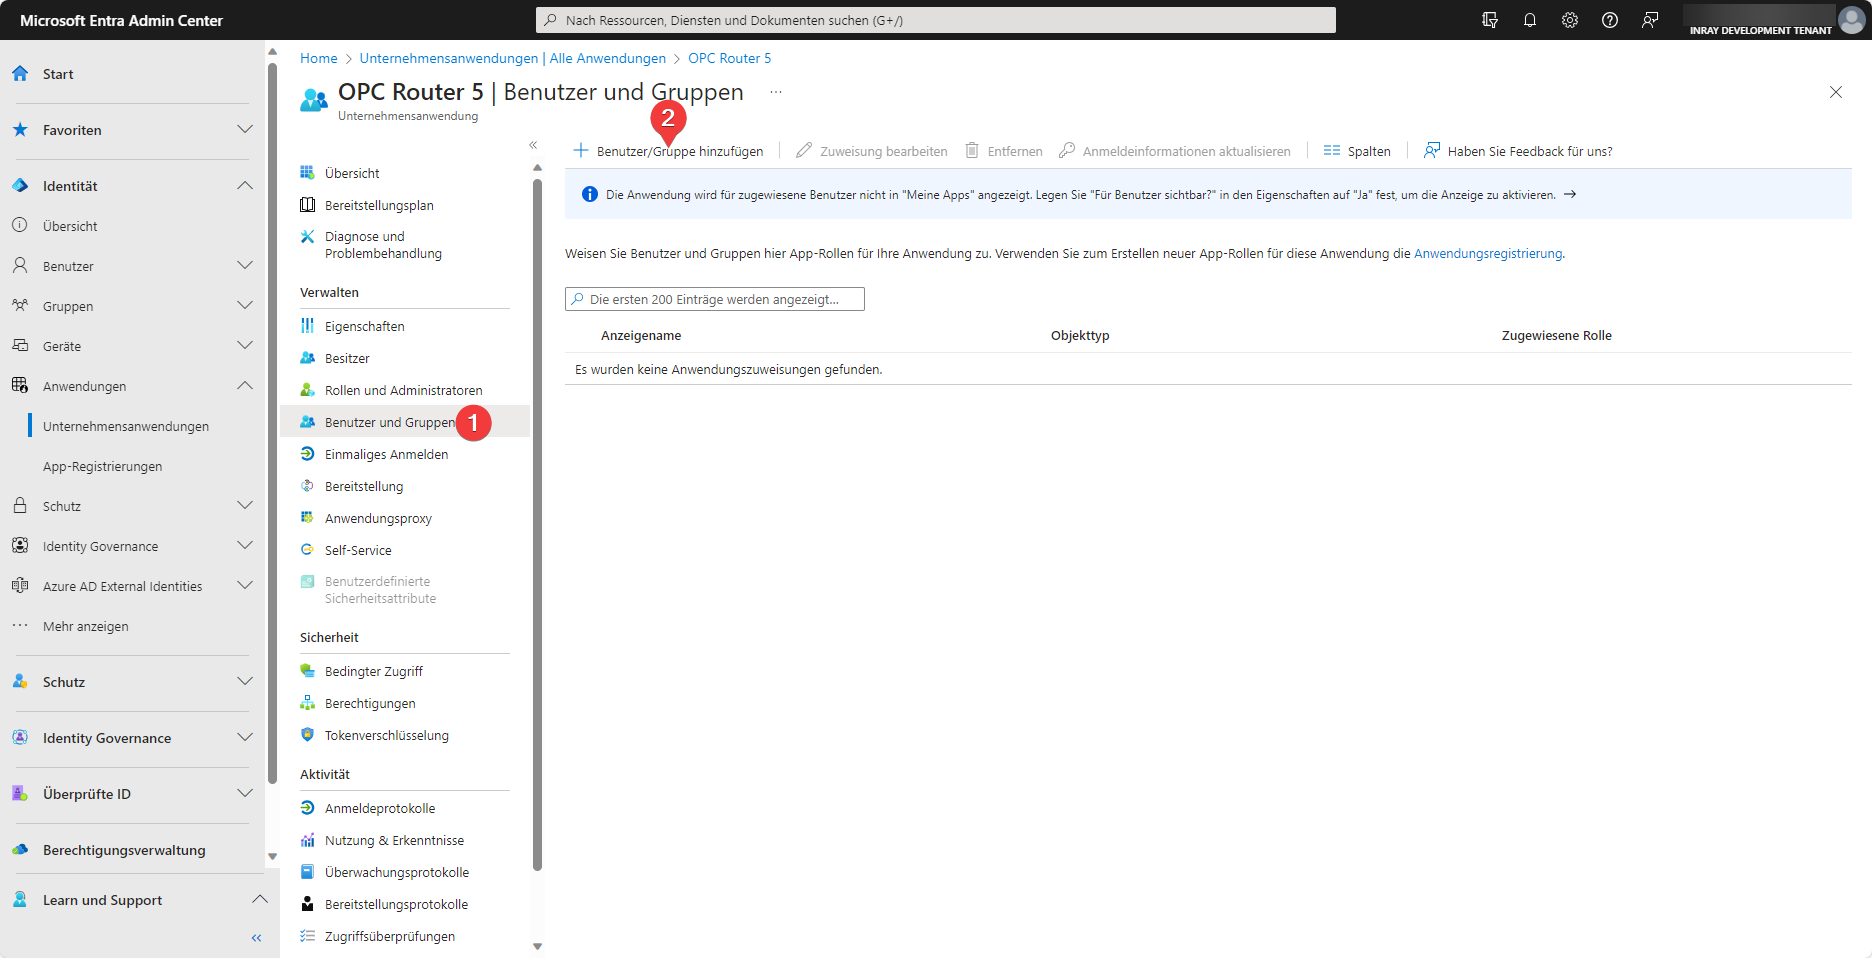
Under the Users and Groups (1) tab, you can then assign roles to users (2).
Users without assigned roles will continue to act as Admin. Simply creating roles is not enough—it is only through assignment that permissions are restricted.
Therefore, explicitly assign a role here to every user who should be able to log in. If this cannot be guaranteed without exception, additionally set AZURE_AD_DISABLE_AUTO_PROVISION=true: This ensures that only users who are already created as external users in the OPC Router can log in, and any overlooked user will not be granted access with administrator privileges.
Changes to user roles are not immediate. Existing saved login tokens (stored in browser cookies) remain valid with the previously assigned roles until they are either deleted or revalidated. This occurs upon logging out and then logging back in.
Assigning multiple roles to a single user is technically possible here. This does not cause errors but currently serves no purpose. Since permissions are additive and the current roles are structured in a strict hierarchy, assigning multiple roles is equivalent to assigning only the highest of those assigned roles.